Currently, you can create tokens with the credentials of Users with activated MFA via our API. This behavior is deprecated due to security concerns. We will remove that feature in the future. You can already deactivate it in the feature settings.
Users with activated MFA will not be able to login in to the Simplifier Client or your Business Applications. If you want to enable it also for Business Apps, you have to use a third-party Identity Management Provider like Azure Entra ID.
Prerequisites
To enable MFA you have to
- use Simplifier as User-Management and every User has to activate MFA on his own user profile
- use a third party Identity Management that offers MFA like Azure Active Directory or Keycloak
Administrators cannot enable MFA for all users, because every user has to enable MFA with an Authenticator App on his personal device.
The built-in 2 Factor Authentication is only available for the Simplifier Administration Interface not within Business Apps. If you want to enable it also for Business Apps, you have to use a third-party Identity Management Provider like Azure Entra ID.
If the User is being managed by Simplifier itself and not by a third-party Identity Management, the User can activate MFA within his User Profile.
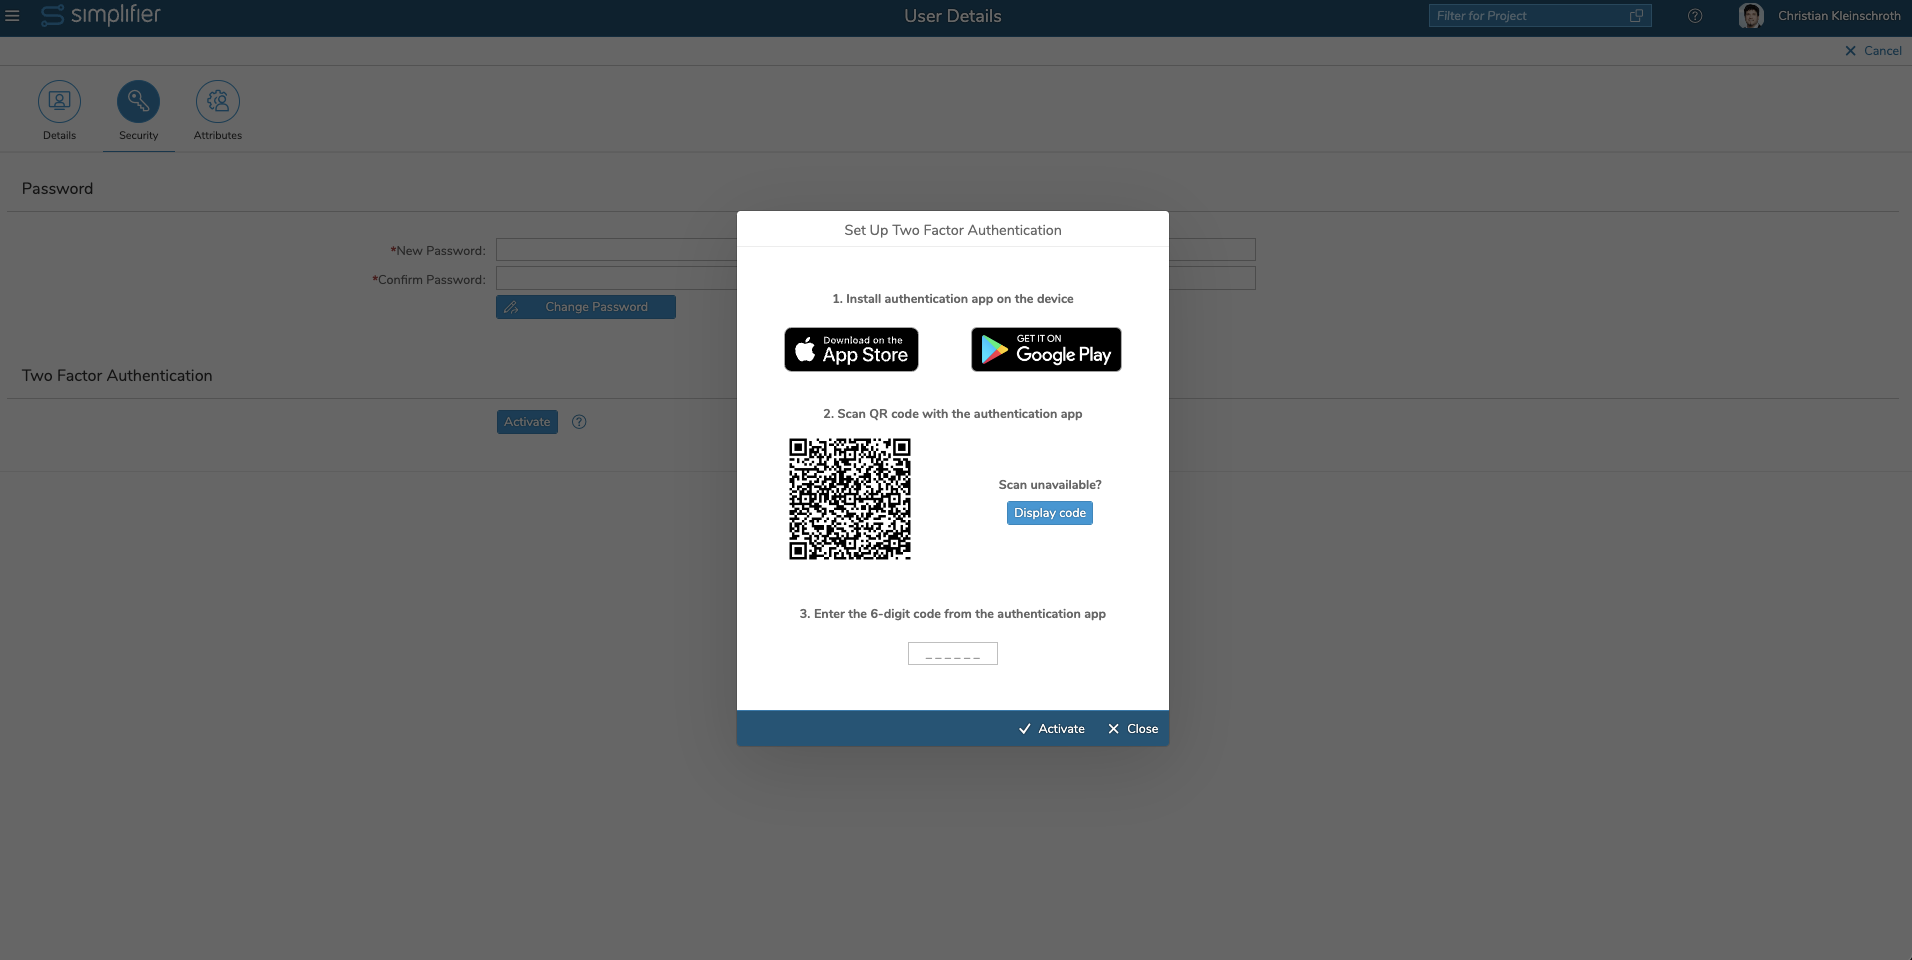
Under the Tab Security, you can activate the Two Factor Authentication by click on activate
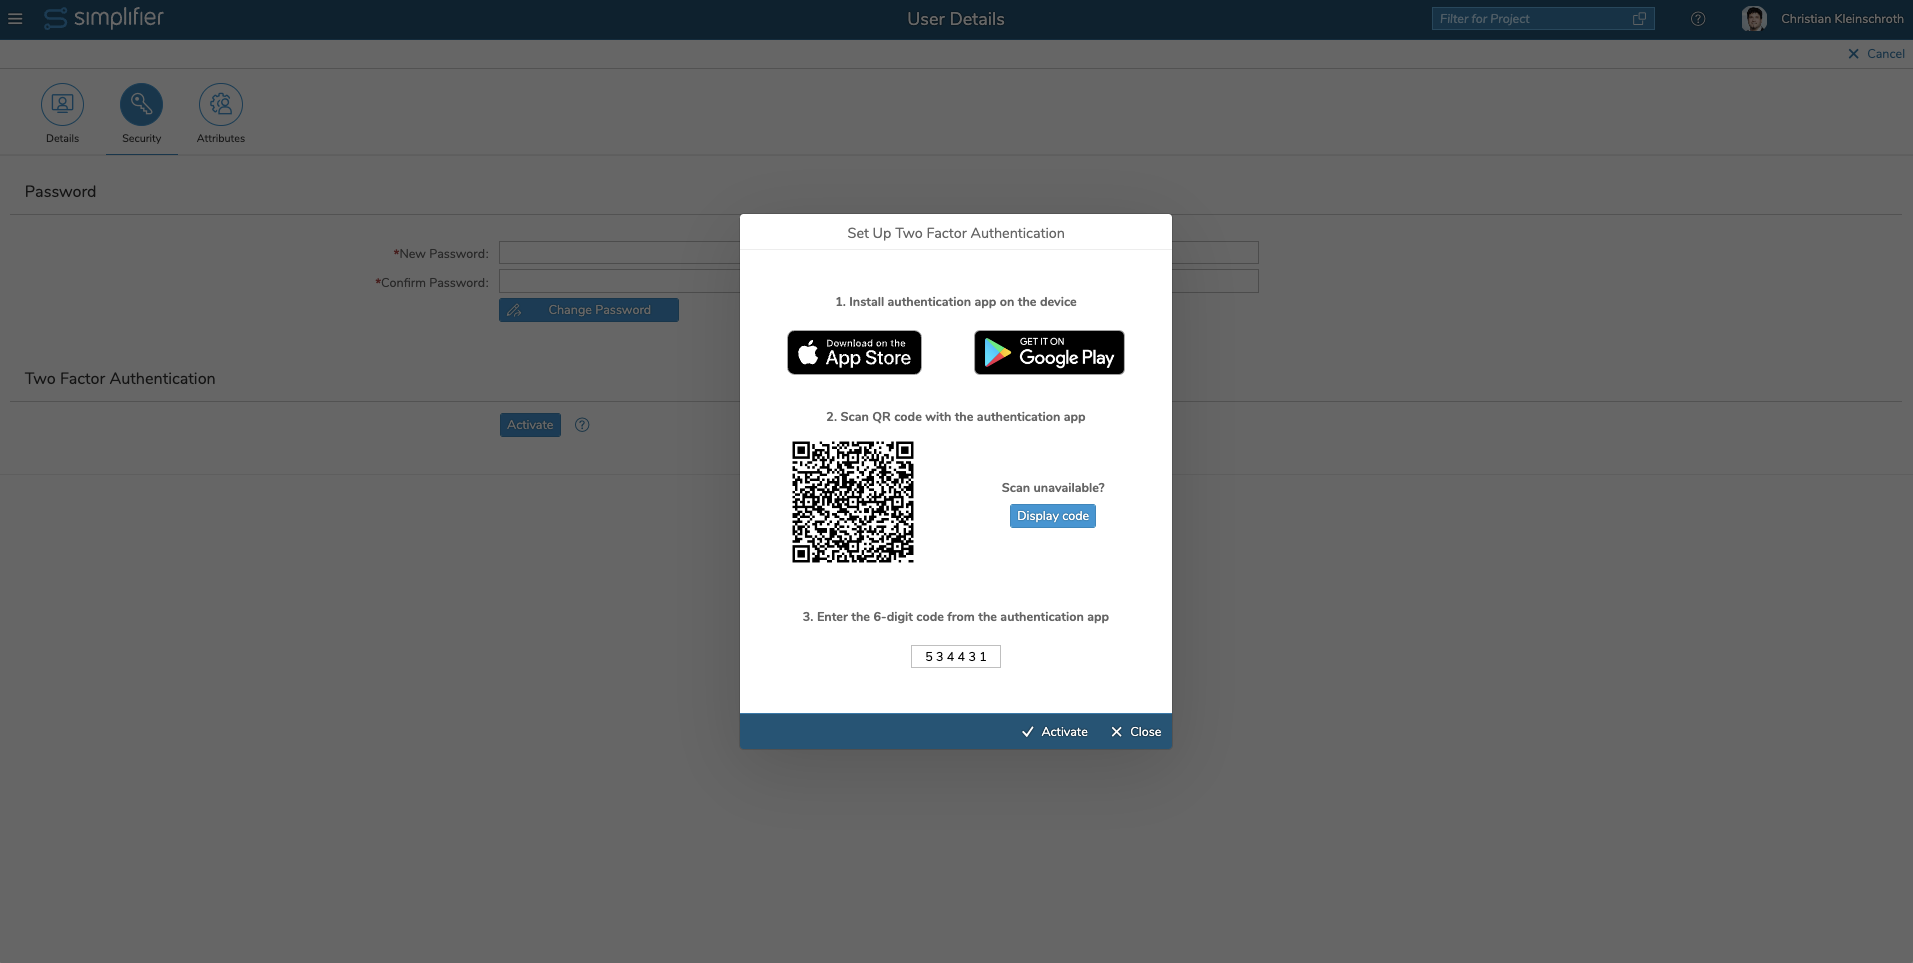
Scan the QR-Code with your previously installed Authenticator App and enter the first generated code to verify the setup.
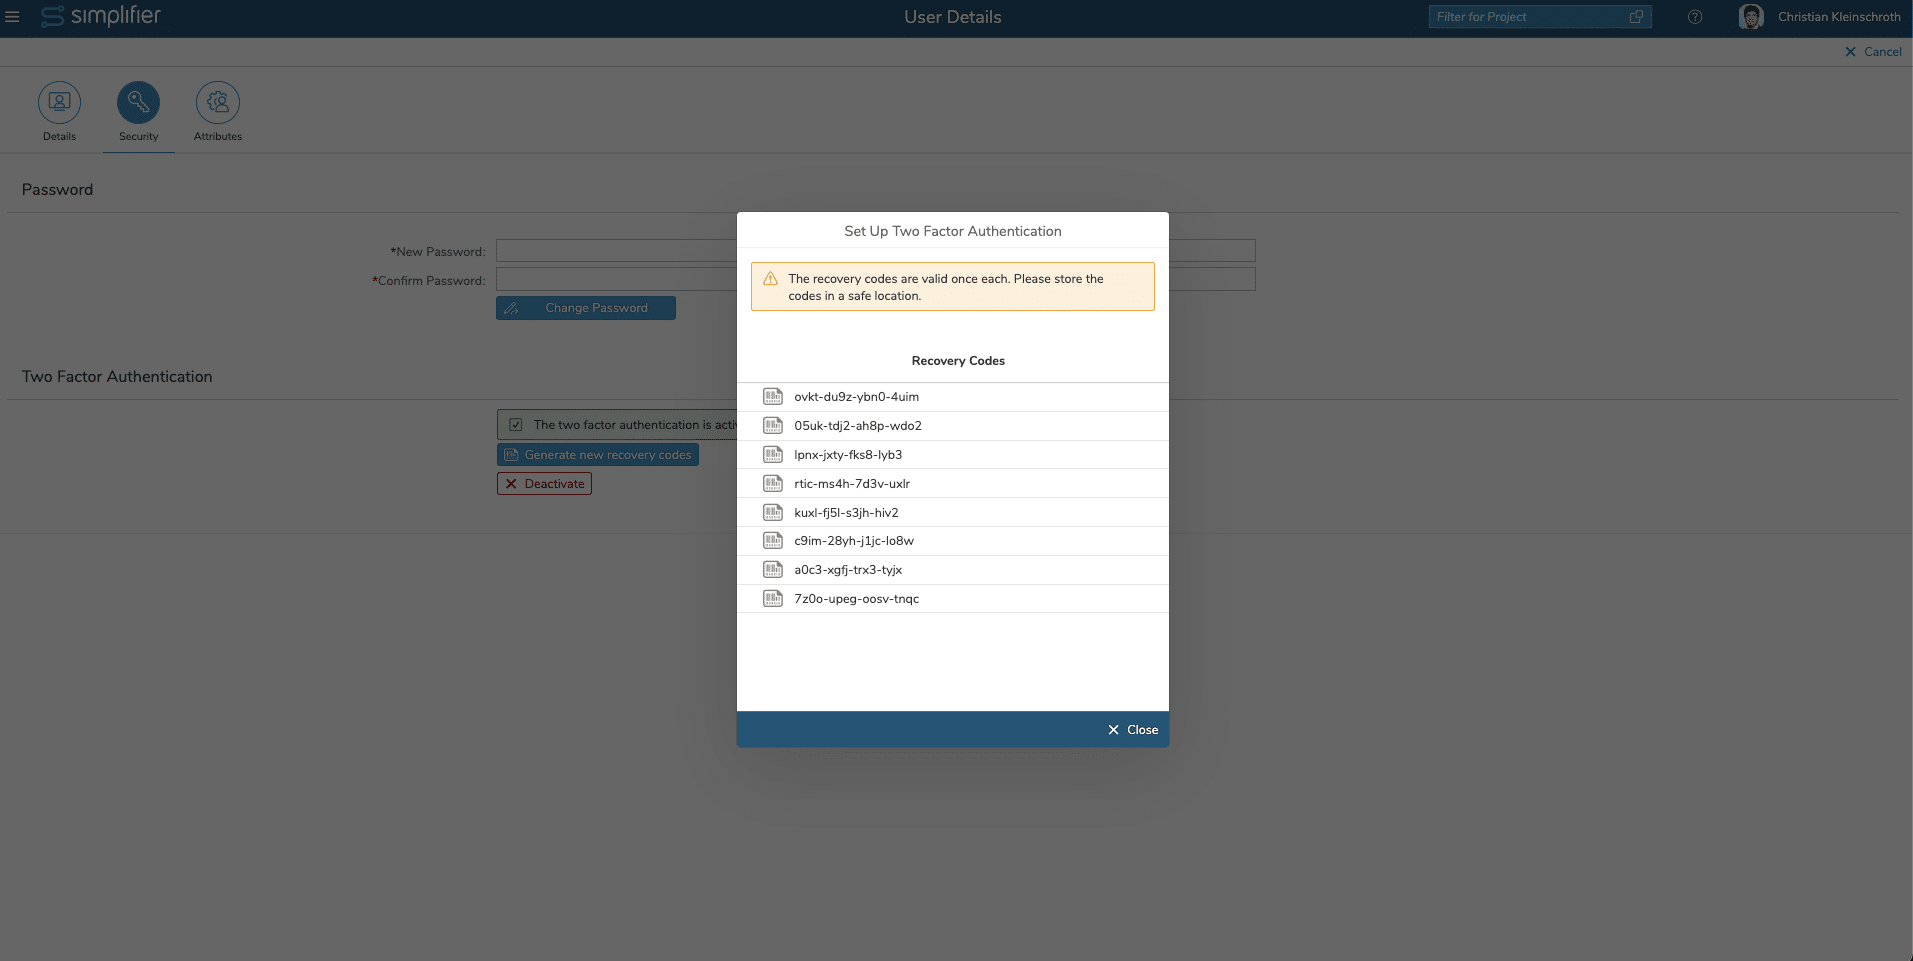
In the next screen, you will receive backup-codes in case your device including the app is getting lost – please save this code via copy & paste into a password manager or secure storage.
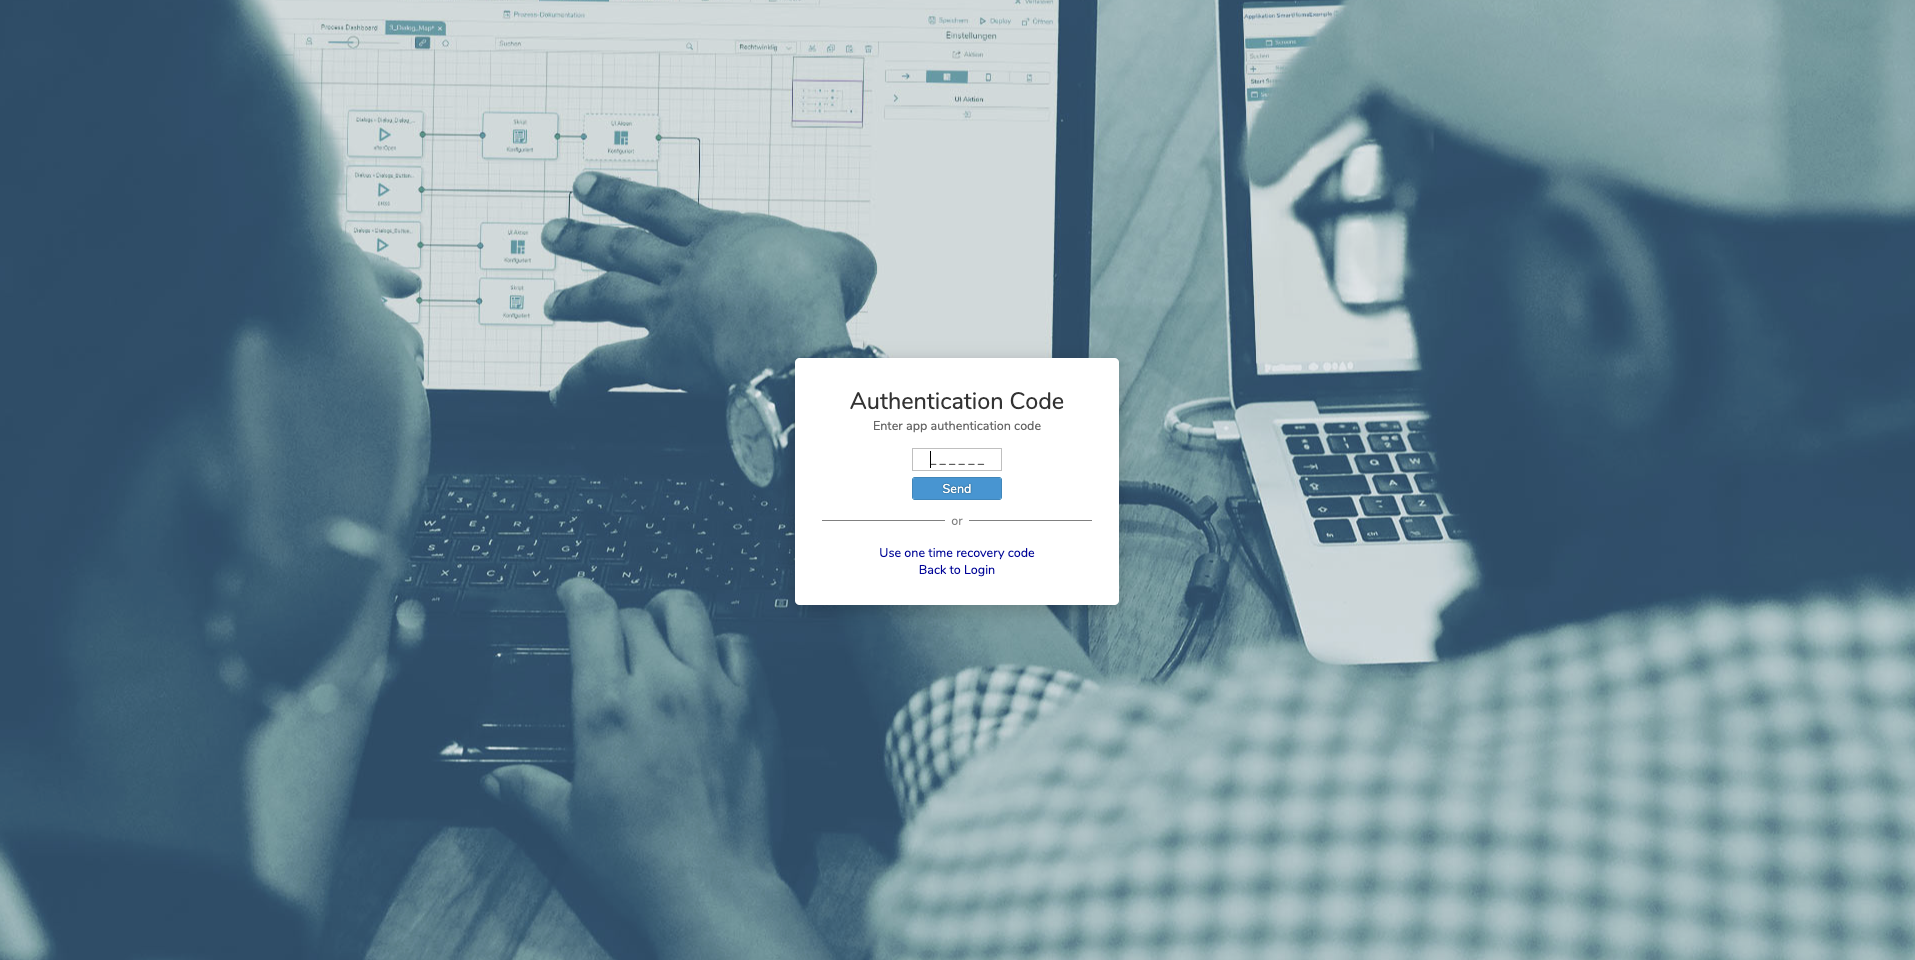
This is all you have to configure. If you login again into Simplifier Administration Interface, you will be asked after enter the password for the additional factor – the generated code.